For years, security operations centres have been caught in an exhausting loop. More threats, more alerts, more fatigue. And never enough skilled analysts to keep pace. The volume and sophistication of attacks have outgrown the capacity of traditional rule-based automation. This leaves organisations perpetually reactive. These environments demand proactive, adaptive defence. Something had to give. In 2025 and 2026, that something is the emergence of AI agents in security operations. These are autonomous or semi-autonomous software systems. They are capable of perceiving their environment, making decisions, and executing security tasks without requiring continuous human intervention.
This is not simply a faster version of what came before.
AI agents represent a fundamental shift in how security is orchestrated. It carries significant implications for security technology providers, enterprise security teams, investors, and the broader digital infrastructure ecosystem.
From Automation to Autonomy: What Makes AI Agents Different
The distinction between traditional automation and agentic AI is not semantic, it is structural. SOAR platforms and scripted playbooks follow instructions. They execute predefined responses when a specific condition is met. AI agents, by contrast, reflect, reason, and adapt. They can ask whether a pattern resembles something encountered before, determine the most appropriate next step given current context, and act within defined guardrails without waiting for a human to approve each move.
This shift as one of the most commercially significant developments in the security industry.
The report positions AI agents as the largest growth opportunity in the sector. The projected market size exceeding $1 billion within five years. It is applicable across every major industry and geography. Gartner’s 2025 Hype Cycle for Security Operations places AI SOC agents at the Peak of Inflated Expectations. This acknowledges both their transformative promise and the caution required in deployment.
Separately, Deloitte’s 2025 forecast predicts that 40% of large enterprises will deploy AI agent systems in their security operations centres within the next year. This pace of adoption signals genuine market momentum rather than speculative interest.
Where AI Agents Are Creating Impact Across Security
AI agents are not confined to a single security domain. We have mapped their application across three distinct verticals – physical security, identity security, and cybersecurity; each with its own operational logic and commercial opportunity.
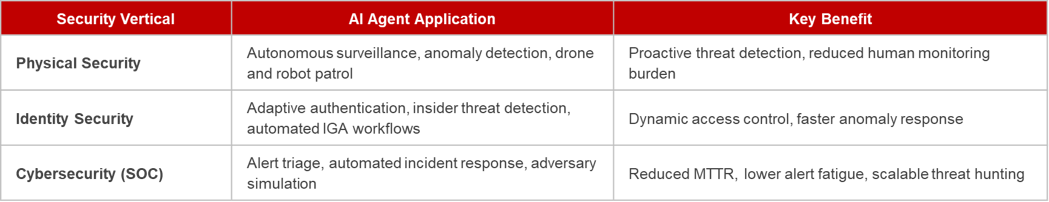
In physical security, AI agents are moving environments beyond passive surveillance. Autonomous drones and ground robots use computer vision and edge analytics. They patrol large perimeters, detect anomalies, and respond to incidents. They do this without waiting for a human controller.
Axis Communications and Motorola Solutions have both deployed AI-powered systems. In these systems, agents generate real-time metadata and trigger automated alerts This meaningfully reduces dependence on human operators. It applies in high-footprint environments such as hospitals, utilities, and transportation hubs.
In identity security, the value of AI agents is most apparent in the management of privileged access. AI-driven systems now continuously monitor user behaviour, device provenance, and environmental signals. They dynamically adjust access rights based on real-time risk assessments. The rise of agentic identity protection is gradually closing gaps. Static credential checks leave these gaps open. Here, AI agents autonomously detect deepfake login attempts. They also respond to identity threats in real time.
In cybersecurity, the impact is most immediate. AI SOC agents already demonstrate the ability to reduce overall alert volume by 50% or more, according to industry analysis, by automatically investigating and closing low-fidelity alerts while escalating the ones that require human judgement. The AI Security Operations Centre (SOC) market reflects this momentum which is projected to grow from approximately $18.10 billion in 2026 to $47.07 billion by 2031. Meanwhile, Gartner’s 2025 survey data shows that 42% of organisations are already piloting or using cybersecurity AI assistants, with another 46% planning to enable them within a year.
The Agent-to-Agent Advantage
Perhaps the most strategically significant development underpinning the opportunity for AI agents in security operations is the emergence of structured agent-to-agent communication. This is a disruptive force reshaping both efficiency and responsiveness in security operations. Rather than isolated agents executing narrow tasks, providers are building the next generation of security platforms around agents that share threat insights, coordinate responses, and adapt in real time across monitoring, detection, and remediation functions.
This is no longer theoretical. In April 2025, Google launched the Agent2Agent (A2A) protocol, an open standard that allows AI agents to securely communicate and coordinate actions across enterprise platforms, regardless of the underlying vendor or framework. Built on enterprise-grade authentication and existing web standards, A2A provides the foundational infrastructure that multi-vendor security ecosystems require to move toward coordinated, autonomous defence architectures. When specialised agents – one monitoring network telemetry, another managing identity signals, a third correlating physical access events can exchange insights at machine speed, the outcome is a security posture that reacts to complex, blended threats far faster than any single human or point solution can.
By 2027, 50% of global security operations will use AI for autonomous and human-in-the-loop responses. The report also projects that broader AI-powered ecosystems will absorb over 60% of point security solutions within two years, as platform consolidation accelerates and integrated agent architectures become the competitive standard.
The Challenges That Cannot Be Ignored
The commercial case for AI agents in security is compelling. But the risks attached to their deployment are equally real. Organisations must acknowledge them with the same seriousness. LevelBlue’s security experts note that agentic AI is already functioning as an “attack surface multiplier”. A single compromised model or poisoned dataset can trigger cascading failures. Traditional malware could never achieve at comparable scale. Threat actors are simultaneously leveraging agentic AI. They generate multilingual phishing content, mutate attack payloads per target, and mine stolen datasets. They do this at a scale that manual tradecraft could never match.
Internally, governance presents its own challenge. Organisations that grant agents broad access to sensitive systems without formal identity management frameworks, data provenance controls, and human oversight mechanisms risk operational failures that are difficult to detect and even harder to reverse. Organisations must develop AI and compliance frameworks alongside capability deployment, not as an afterthought. The firm also notes that regulatory expectations are tightening. These cover transparency, privacy, and algorithmic bias. They span the EU AI Act, GDPR, NIST AI RMF, and CISA guidelines. This creates compliance obligations. Providers must bake these into their architectures from the outset.
What Comes Next for AI-Driven Security Operations?
AI agents in security operations are redefining what security operations can accomplish at scale. Moving beyond the constraints of static playbooks and reactive alert queues, they are enabling security organisations to detect threats faster, respond with greater precision, and extend their defensive reach across physical, identity, and cyber domains simultaneously. The commercial opportunity is large, the adoption signals are accelerating, and the technology foundations including agent-to-agent communication protocols are moving from pilot to production.
What separates organisations that extract genuine value from those that accumulate risk is not the choice to deploy AI agents, but the discipline with which they do so. Human oversight, transparent governance, explainable decision-making, and robust ethics frameworks are not constraints on the agentic future, they are the conditions that make it sustainable.
Understanding how these technologies are evolving and where the next opportunities lie requires a closer look at innovation activity, emerging solutions, and the competitive landscape.
Expertlancing is a global IP research, technology advisory, and market intelligence firm that helps organisations understand complex technology landscapes and make informed strategic decisions. By combining patent data with technical and market insights, Expertlancing helps clients identify emerging technologies, evaluate innovation trends, and uncover potential opportunities across technology domains.
With a team of 60+ professionals in India and a global presence across the USA and Japan, Expertlancing brings together IP researchers and technical experts to examine innovation from multiple perspectives. Whether the objective is to track developments in AI-driven security, assess emerging agentic AI capabilities, or understand competitor R&D activity, its research approach aligns with each client’s specific strategic needs.
Connect with our experts to discuss your research needs and explore how our IP intelligence and technology advisory capabilities can support your next strategic decision.
About The Author